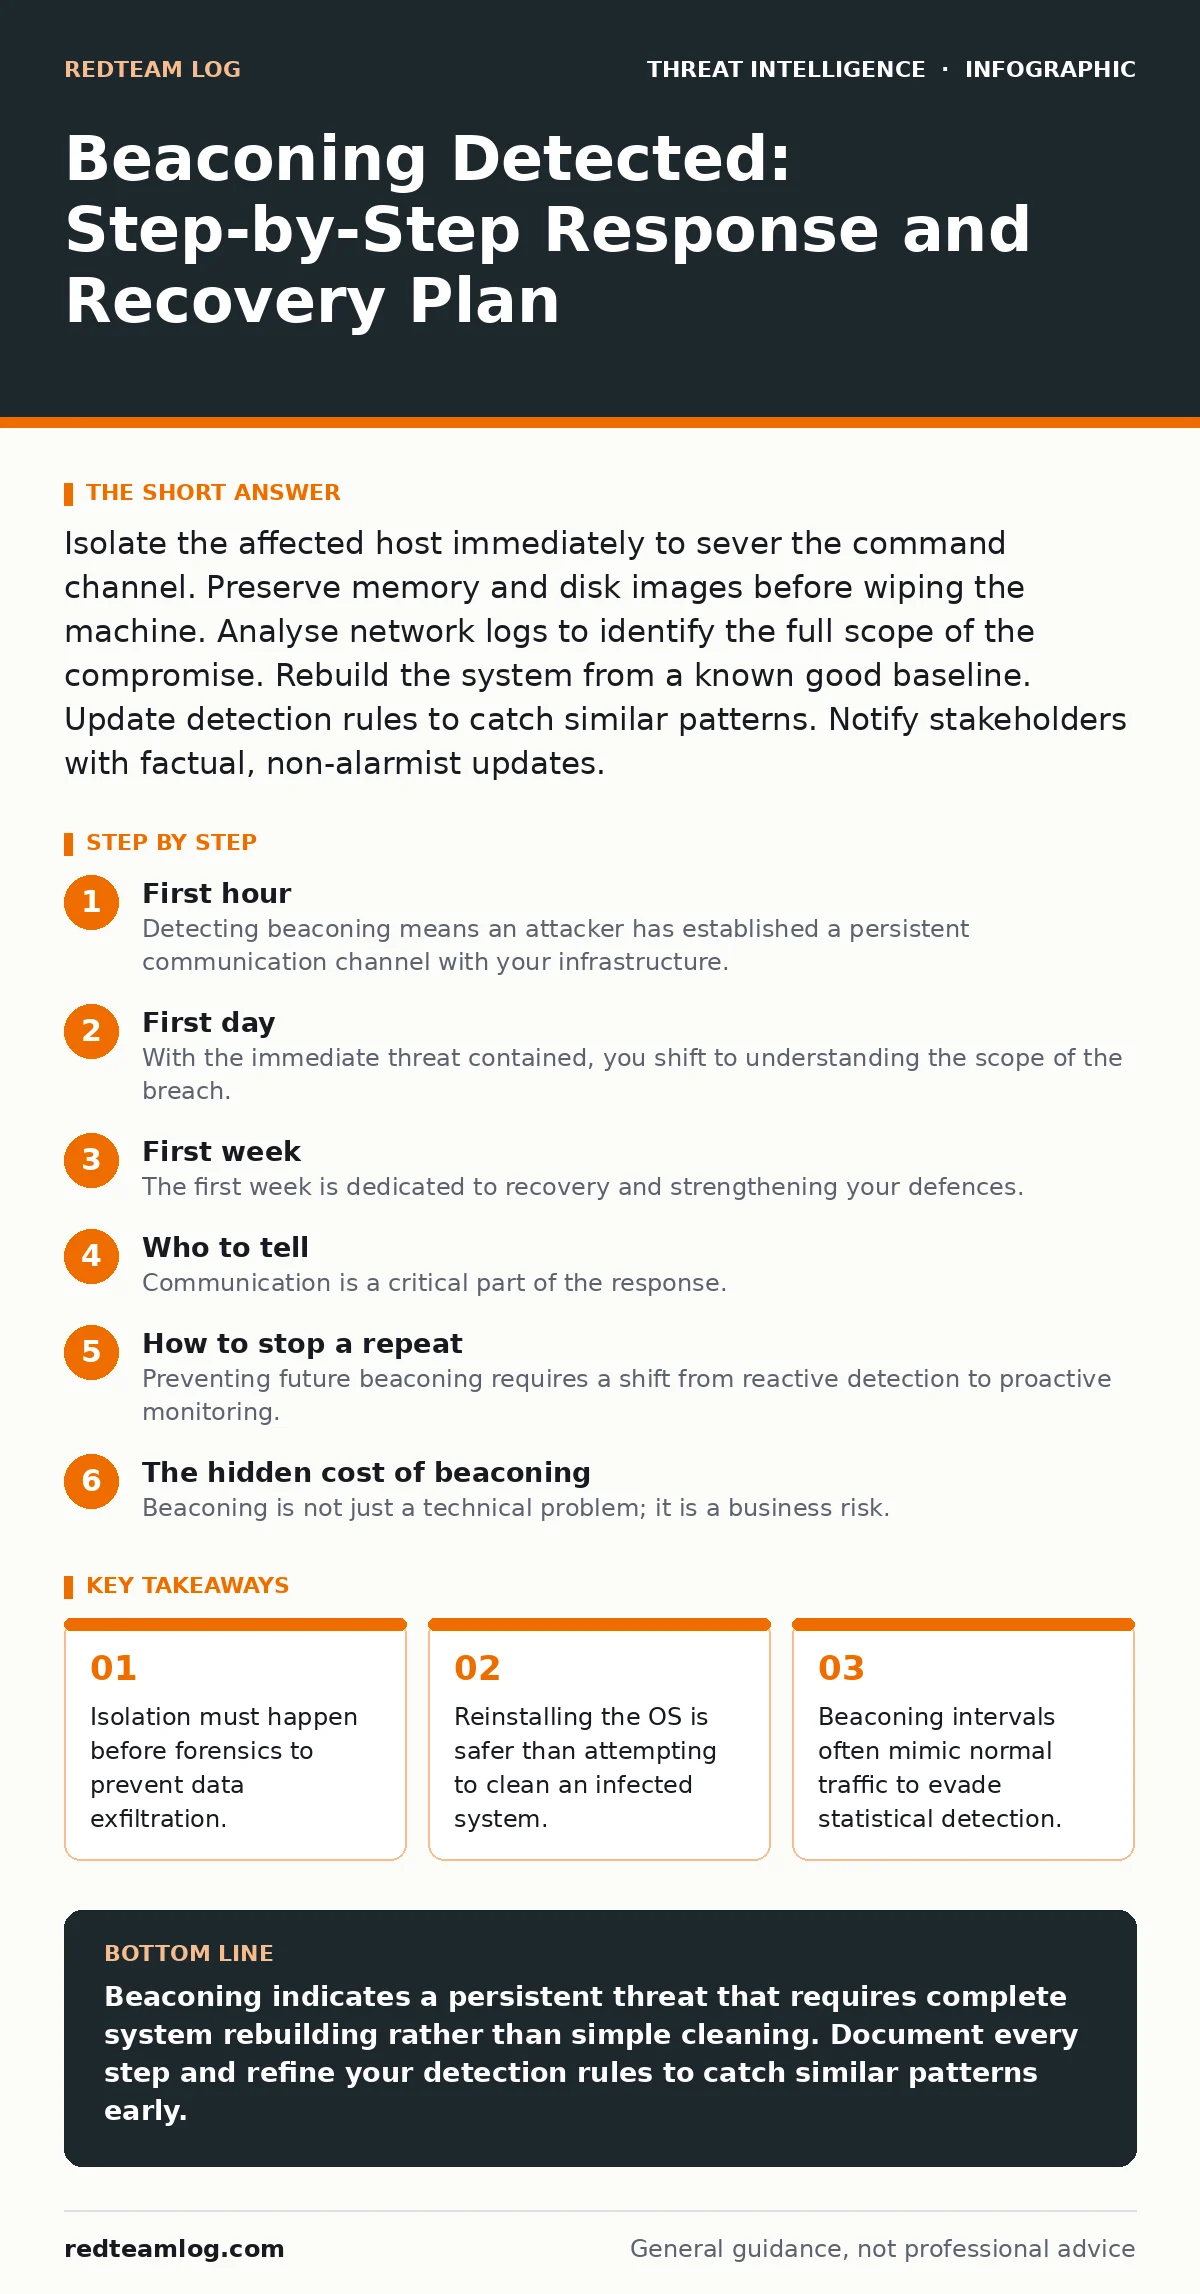
Isolate the affected host immediately to sever the command channel. Preserve memory and disk images before wiping the machine. Analyse network logs to identify the full scope of the compromise. Rebuild the system from a known good baseline. Update detection rules to catch similar patterns. Notify stakeholders with factual, non-alarmist updates.
First hour
Detecting beaconing means an attacker has established a persistent communication channel with your infrastructure. This rhythmic traffic allows them to send commands and receive data without triggering obvious alerts. You must act quickly to limit the damage while preserving evidence for later analysis.
- Isolate the host from the network immediately using port security or VLAN changes.
- Capture a memory dump of the affected system for forensic analysis.
- Block the identified Command and Control (C2) domain and IP addresses at the perimeter firewall.
- Check your SIEM for other hosts communicating with the same indicators of compromise.
- Document the exact time of detection and the initial actions taken.
Isolation is the priority. Once you cut the network connection, the attacker loses their remote control mechanism. This does not remove the malware, but it stops active data theft and further lateral movement. Do not simply pull the network cable, as this may trigger anti-forensics routines in sophisticated malware. Use network-level controls to ensure the isolation is complete and logged.
First day
With the immediate threat contained, you shift to understanding the scope of the breach. Beaconing is rarely an isolated event; it is usually part of a broader intrusion chain. You need to determine how the attacker gained initial access and what else they may have compromised.
Review your logs for the period leading up to the first beacon. Look for unusual login attempts, privilege escalation events or unexpected process creations. Cross-reference these findings with the MITRE ATT&CK framework to map the attacker’s tactics. This mapping helps you understand their likely objectives and potential next steps.
You must also identify all systems that communicated with the C2 server during the beaconing period. Attackers often use multiple hosts to distribute their traffic and avoid detection. Check your DNS logs and proxy records for any other machines querying the malicious domain. If you find additional compromised hosts, isolate them immediately.
Use detection use cases to validate your findings. These predefined scenarios help you spot subtle signs of compromise that might have been missed in initial monitoring. For example, look for processes with unusual parent-child relationships or network connections that deviate from the host’s normal baseline.
First week
The first week is dedicated to recovery and strengthening your defences. You cannot simply clean the infected systems and return to normal operations. The attacker may have left backdoors or modified system configurations to maintain access.
Rebuild all compromised hosts from known good backups or clean images. Do not attempt to disinfect the operating system, as remnants of the malware can survive in obscure system files or registry keys. This approach is more time-consuming but significantly reduces the risk of reinfection.
Update your security tools to detect similar beaconing patterns in the future. Create YARA rules that match the specific indicators of compromise found during the investigation. These rules can help your endpoint detection and response systems catch similar malware strains before they establish persistent connections.
Review your incident response runbooks to see where the process slowed down or failed. Did your team have clear instructions for isolation? Was the evidence preservation step followed correctly? Refine these documents based on what you learned during the incident.
Who to tell
Communication is a critical part of the response. You need to inform stakeholders about the breach without causing unnecessary panic. Tailor your message to the audience, providing technical details to IT staff and high-level summaries to management.
Tell your legal team if the breach involves personal data or regulated information. They can advise on notification requirements and potential liabilities. Notify your cyber insurance provider early, as delays can complicate claims processing.
Inform your clients if their data was accessed or exfiltrated. Be transparent about what happened, what you are doing to fix it, and what steps they should take to protect themselves. Avoid blaming individuals or making speculative claims about the attacker’s identity.
How to stop a repeat
Preventing future beaconing requires a shift from reactive detection to proactive monitoring. You need to understand what normal network traffic looks like so you can spot anomalies more quickly.
Implement network segmentation to limit lateral movement. If an attacker compromises one host, segmentation prevents them from easily reaching other critical systems. This containment strategy reduces the blast radius of any future breach.
Monitor for low-and-slow traffic patterns, which are common in beaconing. Attackers often space their communications out to blend in with normal background noise. Use strategic threat intelligence to stay updated on emerging C2 techniques and adjust your detection rules accordingly.
Be wary of initial access brokers who sell access to networks. These intermediaries often use subtle techniques to avoid detection, making their beaconing patterns harder to spot. Regularly test your defences with simulated attacks to ensure your monitoring is effective.
See also: Router Firmware Vulnerabilities: Response and Recovery Steps · Should I Invest in SOAR? The Truth About Automation ROI
The hidden cost of beaconing
Beaconing is not just a technical problem; it is a business risk. The long-term persistence of an attacker allows them to gather intelligence and plan more sophisticated attacks. This can lead to significant financial and reputational damage.
The cost of recovery is not limited to technical remediation. You must also consider the time and resources spent on investigation, communication and legal compliance. These hidden costs can add up quickly, especially if the breach is discovered late.
Investing in robust monitoring and incident response capabilities is not optional. It is a necessary expense to protect your organisation from the growing threat of persistent network intrusions.
Final checks
Before declaring the incident closed, perform a final review of your security posture. Ensure all compromised systems have been rebuilt and all backdoors have been removed. Verify that your detection rules are working correctly and that your team is trained on the updated procedures.
Document the entire incident, from detection to recovery. This record will be invaluable for future investigations and for improving your security programme. Share lessons learned with your team to ensure everyone understands their role in preventing and responding to similar threats.
Key takeaways
- Isolation must happen before forensics to prevent data exfiltration.
- Reinstalling the OS is safer than attempting to clean an infected system.
- Beaconing intervals often mimic normal traffic to evade statistical detection.
Beaconing indicates a persistent threat that requires complete system rebuilding rather than simple cleaning. Document every step and refine your detection rules to catch similar patterns early.
Frequently asked questions
How long does beaconing typically last?
Beaconing can persist for months or even years if undetected, as attackers often set long intervals to avoid statistical anomalies in network traffic.
Can I clean an infected system instead of rebuilding it?
Rebuilding is strongly recommended because attackers often leave hidden backdoors in system files that are difficult to identify and remove completely.
What is the difference between beaconing and normal traffic?
Beaconing involves regular, predictable intervals of communication with external servers, whereas normal traffic is usually irregular and user-driven.
Should I disconnect the internet entirely?
No, isolate only the affected hosts. Disconnecting the entire network causes unnecessary business disruption and may alert the attacker to your awareness.
How this guide was produced: written by the RedTeam Log editorial team with AI assistance, checked against the public references listed below, and reviewed when the facts change. See our editorial policy or report an error.