Vulnerabilities
Stack Overflow for Agents: ChatGPT Plugin Sparks 10x Agent Creation Rate Surge
OpenAI reports that its new ChatGPT plugin for Stack Overflow for Agents has significantly increased developer signups and agent creation rates.
OpenAI reports that its new ChatGPT plugin for Stack Overflow for Agents has significantly increased developer signups and agent creation rates.
A high-severity nil pointer panic in kin-openapi lets attackers disrupt Go services by supplying specific OpenAPI documents that bypass initial validation checks.
Unauthenticated users can manipulate configuration keys to assume administrator privileges in Misaka Danmu Server versions up to 2.8.9.
Unvalidated inputs in the Claude Agent SDK for Python enable arbitrary command execution, bypassing permission controls before version 0.2.121.
A critical flaw in the ATWINC15x0 driver allows nearby attackers to corrupt memory and execute code via malformed network names.
Researchers demonstrated how chaining two kernel defects allows local users to seize root privileges on OpenBSD systems.
Espionage actors exploited an authentication flaw in BeyondTrust Remote Support to seize full control of appliances and steal credentials.
Unauthenticated attackers can execute remote code via two critical flaws in Next.js caching and image handling, fixed in new LTS releases.
CRLF injection bypasses standard input validation by manipulating HTTP headers, allowing attackers to inject scripts before your browser even renders the page content.
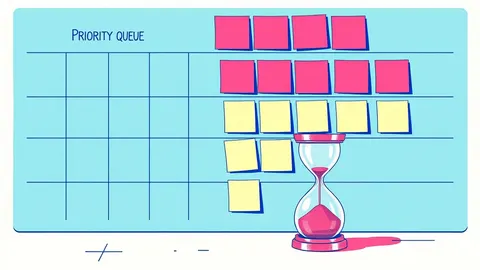
Fixing vulnerabilities by deadline alone wastes resources on low-risk issues while leaving critical systems exposed to active exploitation.
A single misconfigured redirect URI in an OAuth flow can expose every user session to theft without triggering standard intrusion alerts.
Default service configurations expose more attack surface than unpatched software because attackers exploit enabled features rather than broken code.
Silent memory corruption often bypasses standard scanning, making manual code review and strict bounds checking the only reliable defence against out-of-bounds write exploits.
Workflow injection exploits dynamic context parsing to execute arbitrary code, bypassing static security controls and standard input validation checks within your CI/CD pipeline.
The CISA Known Exploited Vulnerabilities Catalog mandates remediation within 120 days of publication, not discovery, creating a fixed window for all organisations.
Zero-click exploits compromise devices without user interaction by exploiting software flaws that execute code before the operating system can verify input safety.
A bug in the open-source server allows attackers to bypass security policies if initialization fails, granting unauthorized access until restart.
Snyk data reveals AI development outpaces security, with malicious packages stealing credentials before scans run.
Rebooting an infected router often fails to remove persistent firmware-level threats that survive standard resets and require full replacement.
Most organisations fail not because they miss vulnerabilities, but because they lose track of fixes, allowing known risks to persist indefinitely.
A critical flaw in nullclaw NullHub allows attackers to rewrite agent configurations and credentials without any authentication, affecting versions up to 2026.5.29.
Attackers can impersonate any user, including administrators, in Znuny versions prior to 7.3.7 by forging a single HTTP request header.
Authenticated admins can run OS commands via a vulnerable content pack, but a patch and mitigation are available.
Palo Alto Networks confirms high-severity flaws in Prisma Browser versions before 155.16.5.40 require urgent updates to prevent session theft.