Data Breaches
User Account Provisioning: Stop Access Drift Before It Costs You
Manual account creation creates invisible permission gaps that automated identity systems close by linking access to real-time employment status.
Everything RedTeam Log has reported about identity management: 6 stories, newest first. Part of our Cloud Security coverage.
Manual account creation creates invisible permission gaps that automated identity systems close by linking access to real-time employment status.
Single sign on centralises credentials within one domain, whereas federated identity delegates trust to external providers, reducing local password management overhead.
Identity sprawl hides in forgotten service accounts and orphaned roles, creating silent backdoors that bypass perimeter defences and persist long after staff leave.
Most cloud security failures stem from misconfigured permissions rather than broken code, making scope definition the single most critical step in any engagement.
Regular password changes often degrade security by encouraging users to select weaker credentials and create predictable patterns that attackers can exploit.
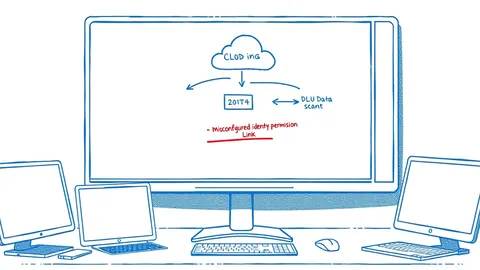
Standard scanning fails against cloud configurations, requiring manual verification of identity permissions and data flow paths to find true exposure.